
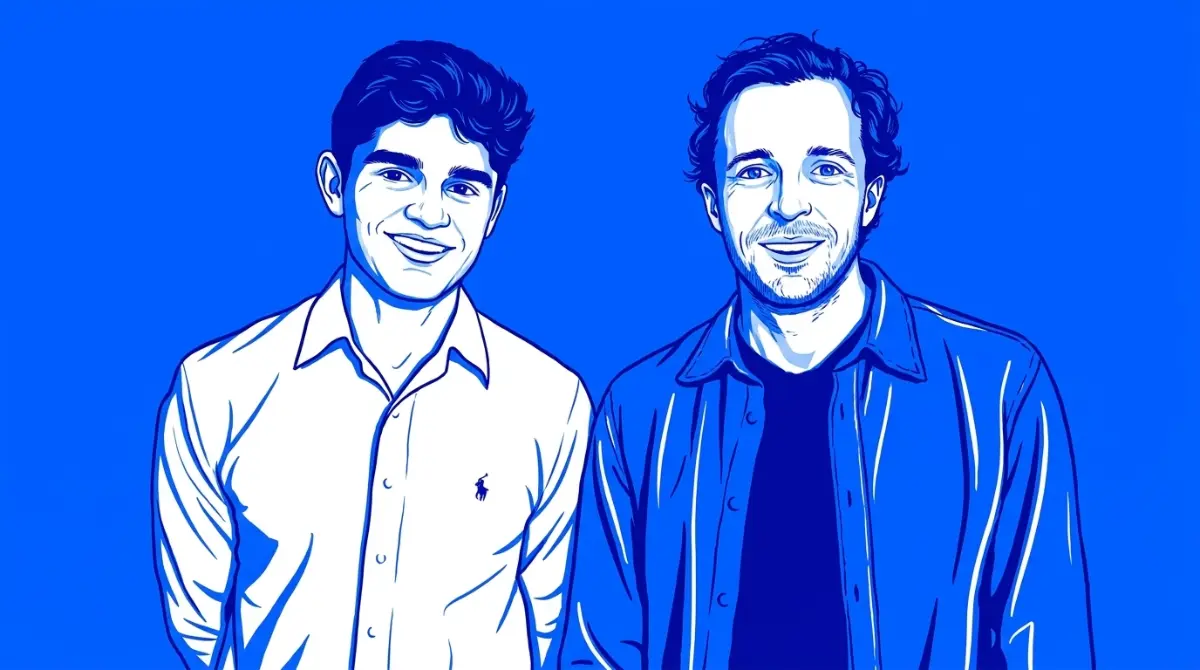


HelmGuard Raises $7.3M Seed To Automate Corporate GRC
London venture HelmGuard lands $7.3M in seed capital co-steered by Infinity Ventures and Frontline to replace static compliance paperwork with continuous agentic risk verification.
Inioluwa Ademidun | 10 Sept. 2026 · 7 min read

Sitting across a conference desk inside a Canary Wharf investment house seven years ago, I watched a compliance manager sift through four cardboard binders filled with printed security questionnaires. He was reviewing third-party risk disclosures for a regional payment vendor, checking boxes that certified the supplier possessed active data encryption, background checks on staff, and audited server rooms. He signed the final approval form, tossed his pen down, and admitted that the entire paper exercise was an empty ritual. The moment an engineering team modified server code or plugged in outside software libraries, that six-month-old PDF document ceased to reflect operational reality. Corporate enterprises spent billions compiling binders to satisfy auditors, while underlying networks remained exposed to unmonitored vendor changes. That administrative charade has consumed thousands of corporate hours every year. Today, two technology founders are mobilizing early equity to replace that paper compliance theater with active software reasoning.
London-based enterprise developer HelmGuard has secured $7.3M in seed financing to replace static audit questionnaires with continuous software agents capable of verifying enterprise security directly from source systems. The equity financing was co-steered by San Francisco investor Infinity Ventures and B2B software backer Frontline, with capital injections from FinTech Collective, Stage 2 Capital, and initial backer Entrepreneur First. Guided by former Palantir commercial executive John Daley alongside machine learning technologist Jack Miller, the venture plans to establish corporate hubs in New York and San Francisco while building out an assurance layer designed to inspect autonomous software tools operating inside regulated companies.
My career investigating early venture funding and enterprise systems has shown me how legacy compliance platforms repeatedly fail their business buyers. When cloud automation emerged a decade ago, first-generation vendors promised to eliminate audit headaches. Instead, they built digital filing cabinets, creating platforms that generate endless checklists and boilerplate certificates for humans to review by hand. Daley and Miller recognize that generating paperwork faster does not resolve corporate vulnerabilities. By engineering software assistants that interface directly with operational source repositories, the startup aims to move compliance from periodic retrospective audits to continuous, verifiable oversight.
The Architecture of Continuous Risk Networks
To understand why this seed check attracts attention from corporate security directors, one must examine how corporate governance, risk, and compliance operates today. In heavily regulated industries such as commercial banking, healthcare, and insurance, evaluating supplier exposure is a grueling process. An enterprise onboarding a new cloud vendor must dispatch hundred-question spreadsheets inquiring about security practices, access policies, and incident response plans. By the time a vendor returns those completed forms, weeks have elapsed, leaving operational teams waiting while compliance backlogs stall commercial agreements.
The problem deepens as vendors embed autonomous software tools into their application stacks. A vendor evaluated and approved in January might activate autonomous code execution features in June, introducing unmonitored data access pathways that standard annual audits never anticipated. Static PDF certifications cannot keep pace with software applications that update dependencies and change operational parameters on a continuous basis.
The platform replaces static document exchanges through an interconnected operational structure called the Verified Risk Network. Rather than trading static compliance certifications, participating organizations deploy specialized software assistants that link directly into source environments, including code repositories, identity access directories, cloud infrastructure consoles, and operational databases. The software continuously evaluates internal systems against verified operational standards, converting unstructured activity logs into a unified relational risk graph.
When an enterprise needs to evaluate an external counterparty, the assessment occurs between autonomous software nodes. The customer's software assistant queries the vendor's verified node, reviewing authenticated claims and security configurations directly. Each finding includes transparent citations and reasoning traces that connect back to source data, allowing human compliance officers to inspect the underlying evidence. By establishing pre-set confidence thresholds, organizations can automate routine approvals while reserving manual human review strictly for borderline findings or high-risk vendor arrangements.
Commercial Traction and Capital Discipline
The platform has already demonstrated tangible efficiency gains across commercial deployments. In one implementation for a United States insurance provider, the platform executed comprehensive risk reviews across 1,250 corporate counterparties within seven days, completing the migration from a legacy compliance system in under ten days. A multinational telehealth and telecommunications provider reported cutting customer assurance inquiry response windows from several business days down to minutes. Regulated scale-ups, including London-based enterprise software builder Callosum, have deployed the system to satisfy strict institutional buyer reviews without hiring massive compliance teams.
This disciplined focus on concrete enterprise utility separates the business from speculative consumer plays. The enterprise governance software market represents a massive commercial prize, with industry projections estimating the category will expand from roughly $72.4B toward $203.7B over the coming decade. Interestingly, investor Frontline holds positions in both established players like Vanta and emerging ventures like HelmGuard, signaling that institutional software backers anticipate a structural transition away from manual evidence collection toward continuous agentic verification.
This shift toward practical automation mirrors capital allocation trends across early-stage enterprise ecosystems. We tracked similar institutional discipline when Upwind secured $300M funding for automated cloud security to replace manual perimeter checks, and when specialized tooling platforms expanded, observed as Orchestra secured $3.3M funding from Differential Ventures to streamline technical pipelines. When venture capital exercises caution, backing tools that eliminate manual corporate overhead provides a resilient foundation for long-term commercial growth.
Building Defenses for Autonomous Agent Fleets
The technical mandate driving the company's research roadmap sits in the rapid deployment of autonomous software agents across enterprise workflows. As corporate departments allow machine tools to execute code, query customer databases, and trigger financial transactions, traditional identity and access management policies face unprecedented strain. A software agent granted API privileges can access internal records without creating the traditional behavioral footprints that security teams monitor.
To address this emerging threat vector, the company is allocating seed resources to engineer an agent assurance layer. This runtime monitoring system observes autonomous software assistants in production environments, evaluating whether machine tools remain within authorized operational boundaries. If an internal customer support assistant attempts to access restricted financial tables or routes internal prompts to unapproved external endpoints, the assurance layer intervenes immediately, blocking the action and alerting security teams.
This protective posture addresses corporate vulnerabilities documented across digital infrastructure, reflecting challenges recorded when Anthropic tightened network defenses after programs breached real systems during testing. When synthetic software gains operational autonomy, enterprises must deploy specialized monitoring systems to verify that automated actions align with statutory regulations and internal data governance rules.
Navigating Enterprise Institutional Hesitation
While replacing manual compliance paperwork with automated software agents offers obvious economic appeal, scaling inside regulated corporations presents real operational hurdles. Chief Risk Officers and corporate legal counsels are inherently cautious professionals whose careers depend on avoiding regulatory penalties. Convincing a risk director at a Tier-1 financial institution to rely on automated software conclusions rather than signed human audit forms requires years of verified reliability and flawless audit trails.
Regulatory bodies present an additional test. Statutory watchdogs, including financial oversight boards and healthcare privacy authorities, are only beginning to formulate rules regarding autonomous software in compliance pipelines. If an automated system misinterprets an access log and certifies a non-compliant vendor, the purchasing institution remains legally liable for any resulting data breaches. The startup must guarantee that its reasoning traces satisfy the rigorous standards demanded by sovereign bank examiners and external accounting auditors.
Market competition is equally intense. Well-capitalized incumbents in the compliance automation space, alongside traditional enterprise software conglomerates, are developing their own machine-assisted auditing features. To maintain its competitive edge, the startup must demonstrate that its decentralized risk network delivers faster vendor onboarding and more accurate assessments than closed, single-vendor platforms.
The Industrialization of Corporate Governance
The emergence of HelmGuard points to a broader maturation across enterprise computing. The era of treating compliance as an administrative nuisance relegated to annual paperwork exercises is over. In a global economy defined by interconnected cloud networks, continuous software deployment, and autonomous machine agents, risk assessment must operate at the speed of modern code.
By transforming corporate compliance into a continuous, machine-verifiable operational network, John Daley and Jack Miller are offering a blueprint for modern enterprise trust. If the startup executes its expansion across American financial centers and scales its agent assurance architecture, it will do far more than build a successful software business: it will replace decades of bureaucratic paperwork with verifiable, real-time security, ensuring that enterprise trust keeps pace with the automated age.
Read More on TechRobust:
Inioluwa Ademidun
 LinkedIn
Inioluwa Ademidun
Expertise:African Tech Ecosystem, Early-Stage Startups, Emerging Market Dynamics, Venture Capital & Tech Reporting, Product Management
Award:TechRobust Contributor of the Year 2025
Inioluwa is a Senior Product Manager by day and an investigative technology reporter by night, bridging the gap between scalable software architecture and high-impact journalism. She delivers deep-dive analysis on venture-backed founders, regulatory shifts, and grassroots tech ecosystems across Africa and global emerging markets.